Nuclear
Nuclear Plant Workers Fired After Digital Credential Breach at Louisiana Site
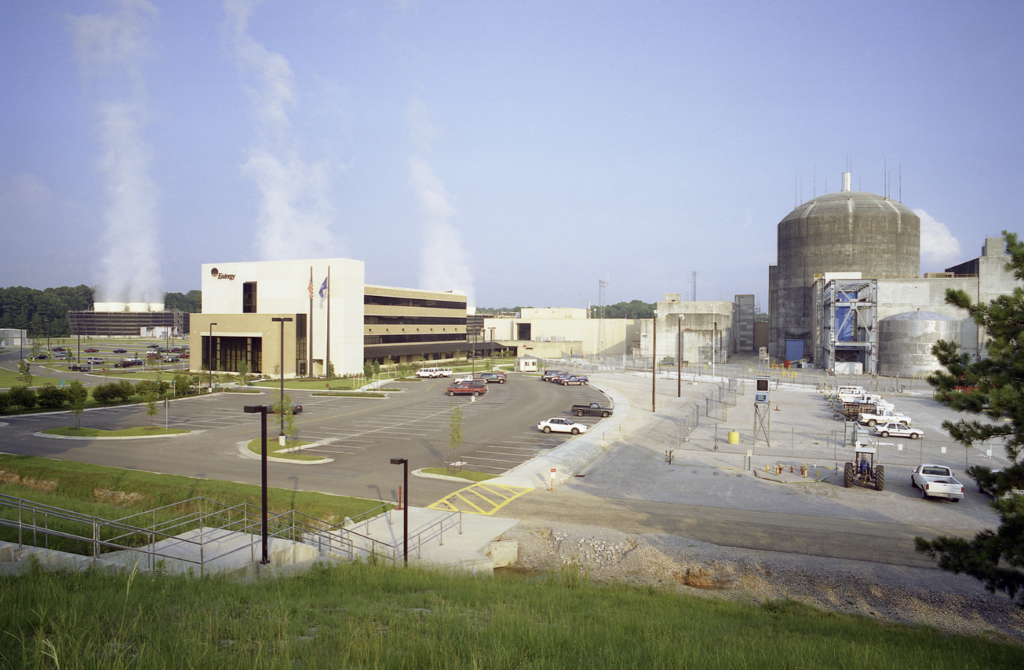
The Nuclear Regulatory Commission revealed this week that it launched an investigation, and two workers at the River Bend 1 nuclear power plant in Louisiana were fired after a plant supervisor handed over highly secured digital credentials to an outside contractor.
The incident, which the NRC said happened last year, involved a supervisor at the nuclear site handing over the cyber credentials, or “critical digital asset” (CDA) key to the contractor. The NRC said it found the supervisor and contractor engaged in “deliberate misconduct.”
The regulatory commission completed its investigation in May 11, and posted the result to the NRC website on Friday.
“On September 9, 2025, the maintenance supervisor checked out, to himself, a CDA key that was needed for work at the access authorization building, outside of the secure owner-controlled area (SOCA),” the NRC wrote in a letter to an executive at Entergy, which owns and operates the River Bend 1 site.
“After this work was complete, the maintenance supervisor gave the CDA key to a contractor, who was not qualified as a critical group member, for the purpose of returning the CDA key to the kiosk repository.
“The maintenance supervisor also gave his own access badge to the contractor, in order to scan the CDA key back into the kiosk,” the NRC wrote.
The supervisor knew the contractor was not part of a small group of employees cleared to have the credentials, the NRC said.
“When questioned, the maintenance supervisor admitted to knowingly transferring the badge and key, citing that time constraints and familiarity with the contractor influenced their decision,” the NRC said.
Nuclear power plants in the U.S. are staffed by both payrolled employees, who run and oversee a plant and reactor’s operations, as well as outside contractors who often move from plant to plant working on tasks involving plumbing, electrical work, equipment replacement, and refueling, as well as numerous other tasks.
Regulations call for tight security and credentialing requirements at these plants; cybersecurity rules—which are also strict—are in a category of their own.
They include items including control over digital keys as well as other issues like prohibitions against scrolling the Internet for personal use inside protected areas at a nuclear power plant.
The NRC said it is still weighing how serious of a rules violation to categorize the incident, but noted they consider it a willful violation.
“Willful violations are of particular concern because the NRC’s regulatory program is based on licensees and their contractors, employees, and agents acting with integrity and communicating with candor. The Commission cannot tolerate willful violations,” regulators noted in their letter to Entergy.
Leave a Reply